AI compliance you can prove
Bay maps every agent and policy to the frameworks you report against, with a complete audit trail and board-ready reports behind them.
Why AI policies are hard to prove
Most organizations have an AI policy. Few can prove it’s enforced, or show what their agents actually did. When auditors or regulators ask, that gap shows, and AI adoption stalls until it’s closed.
Bay turns your policy into guardrails and records the evidence as it happens, so you can scale AI and still answer every question.
How it works
Set policies that follow each team
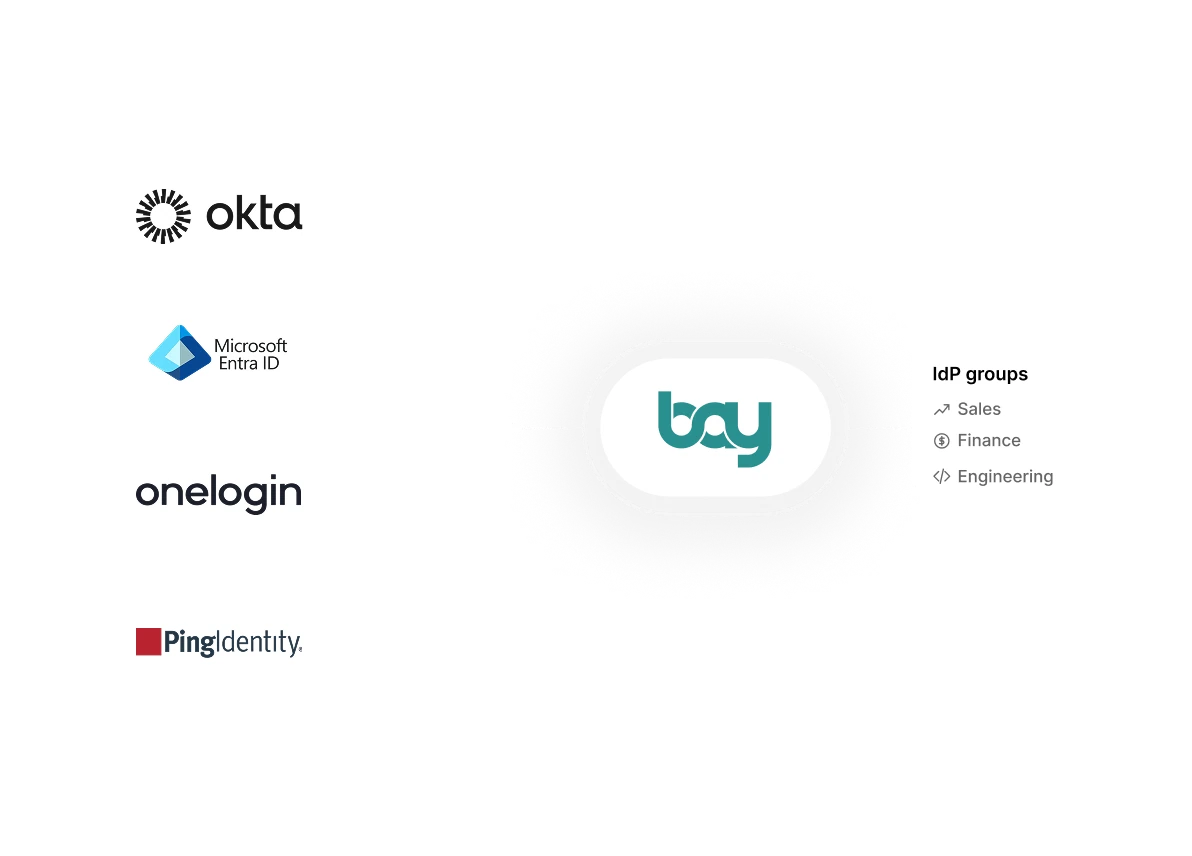
Bay connects to your identity provider, so every policy applies to the right people and groups, and keeps up as your organization changes.
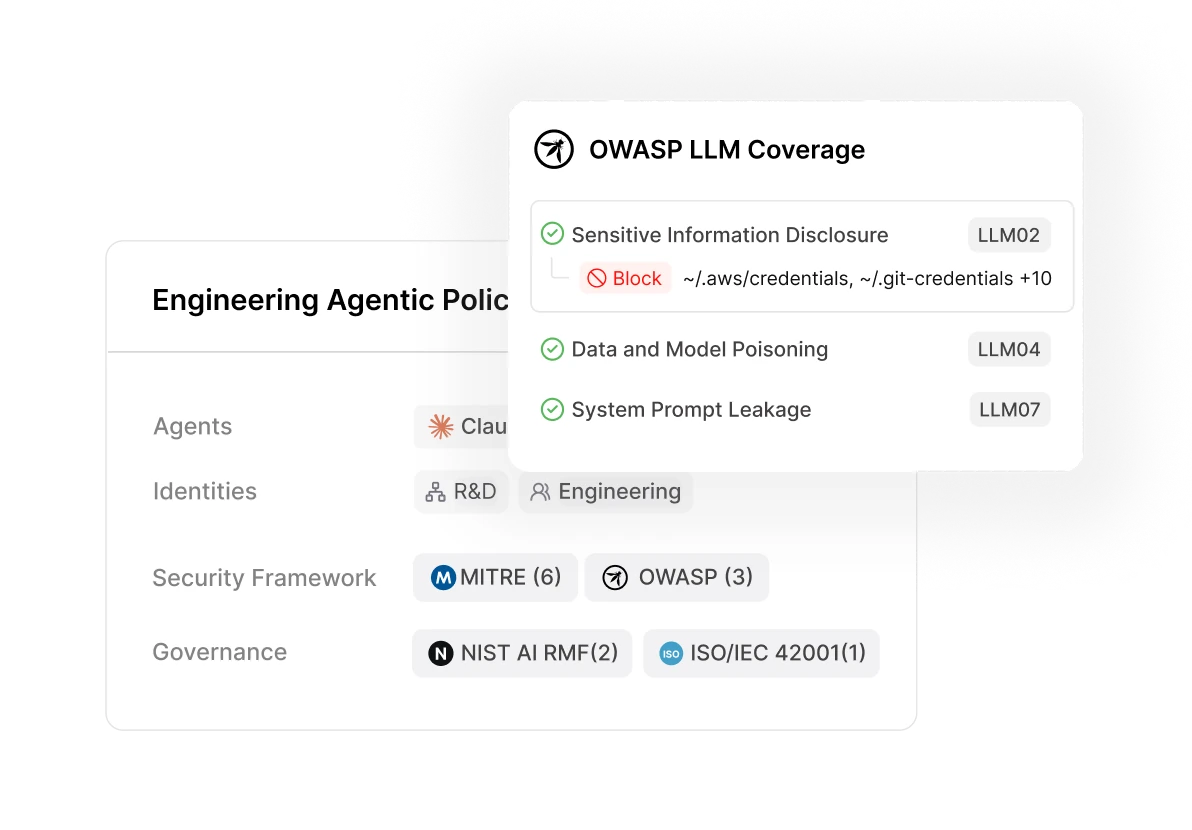
Map every control to the frameworks you report against
Bay links your policies and the activity behind them to the OWASP LLM Top 10, NIST AI RMF, MITRE ATLAS, the EU AI Act and ISO/IEC 42001, so findings arrive in the language your auditors use.
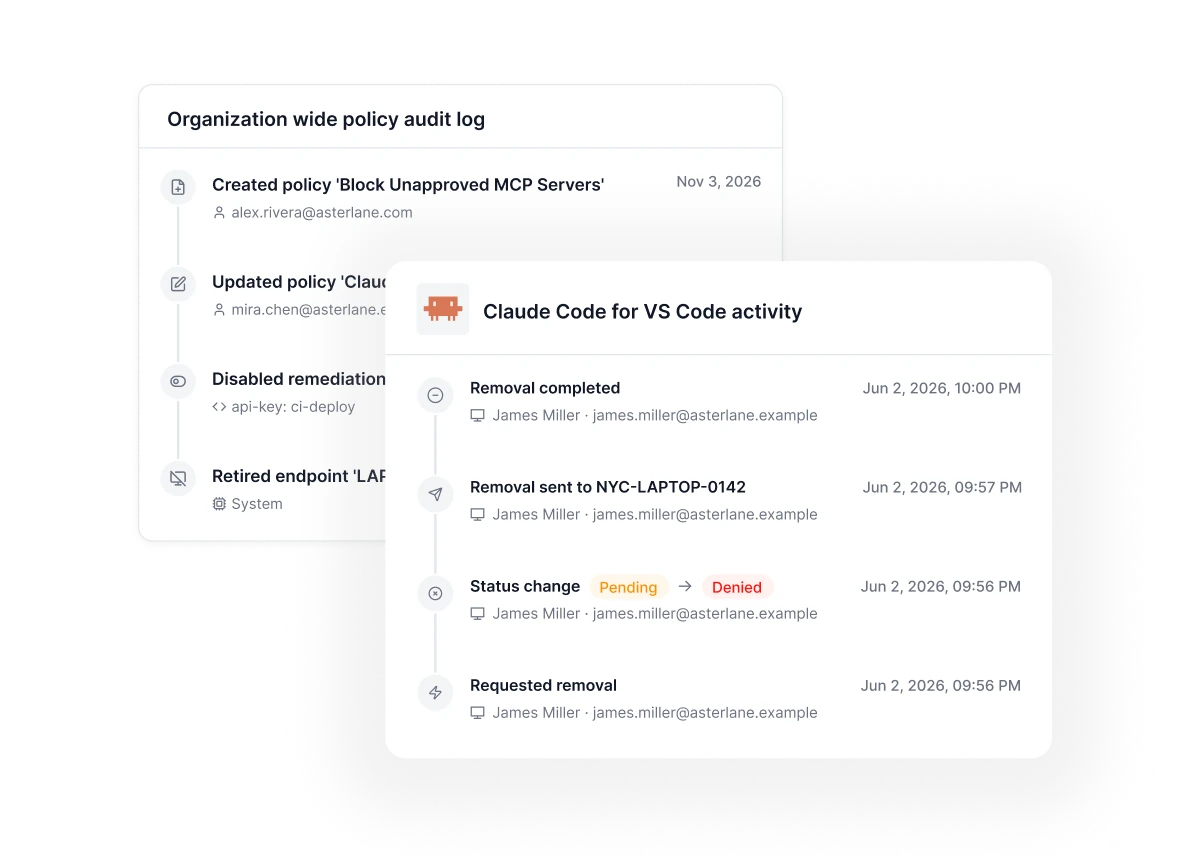
Keep a complete record your auditors can rely on
Every policy change and agent action is logged with who approved it and whether a person or an agent took it. That’s the accountability SOC 2 depend on.
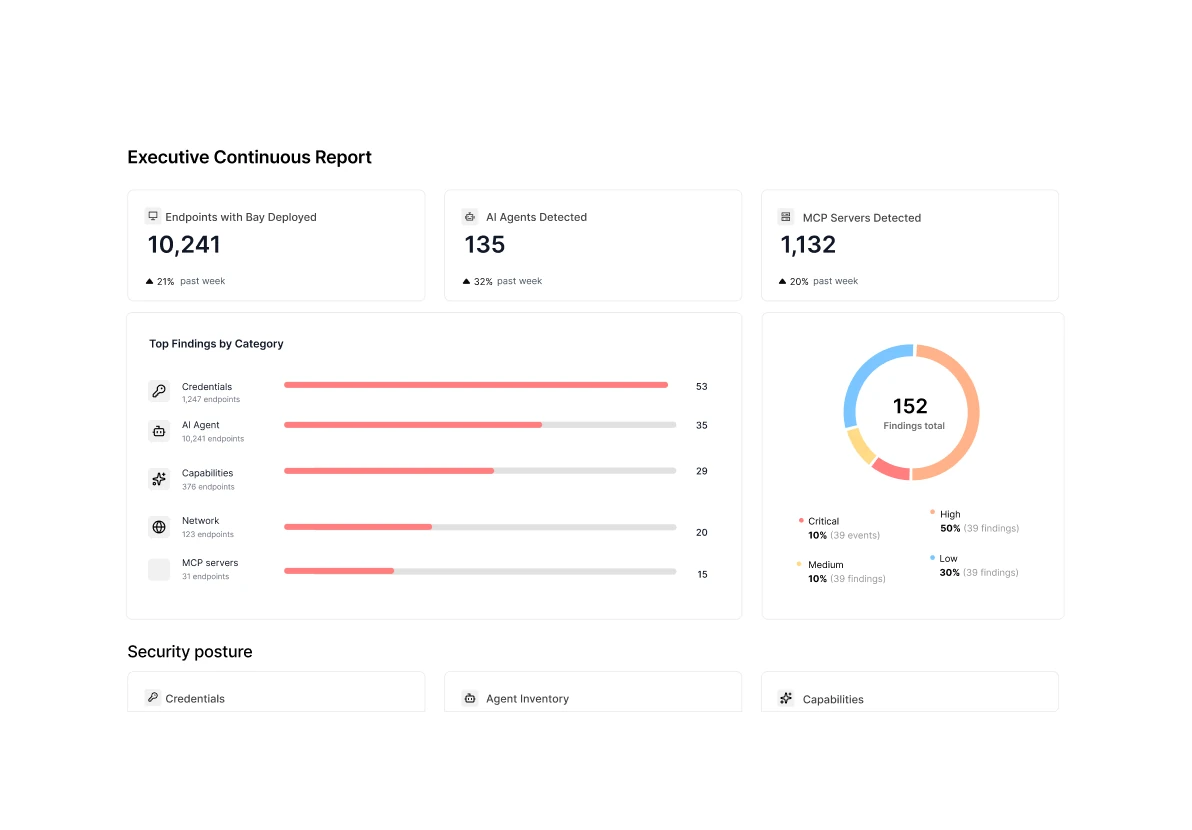
Give the board a clear answer on AI risk
Board-ready reports show how AI is used across the organization and where policy violations were stopped, written so no one needs a security background to follow them.
Live in 5 minutes. Tailored in an hour.
Works with your stack without replacing it.